
NEW DELHI, October 9, 2026, 5:11 PM IST — Google Cloud has launched Gemini agent, a universal work agent designed to plan and complete multi-step jobs across business systems, developer tools and productivity apps while operating under centralized identity, policy, audit and spending controls.
The announcement moves Google’s enterprise AI pitch beyond a conversational assistant. Gemini agent can run for hours or days in the cloud, create temporary sub-agents, write and execute code, use business data and return completed work inside environments including Google Workspace, Microsoft 365, Slack and command-line tools. For platform teams, the consequential part is not another chat interface but the attempt to give autonomous software the same operational controls expected for human and service identities.
One agent, multiple models and long-running work
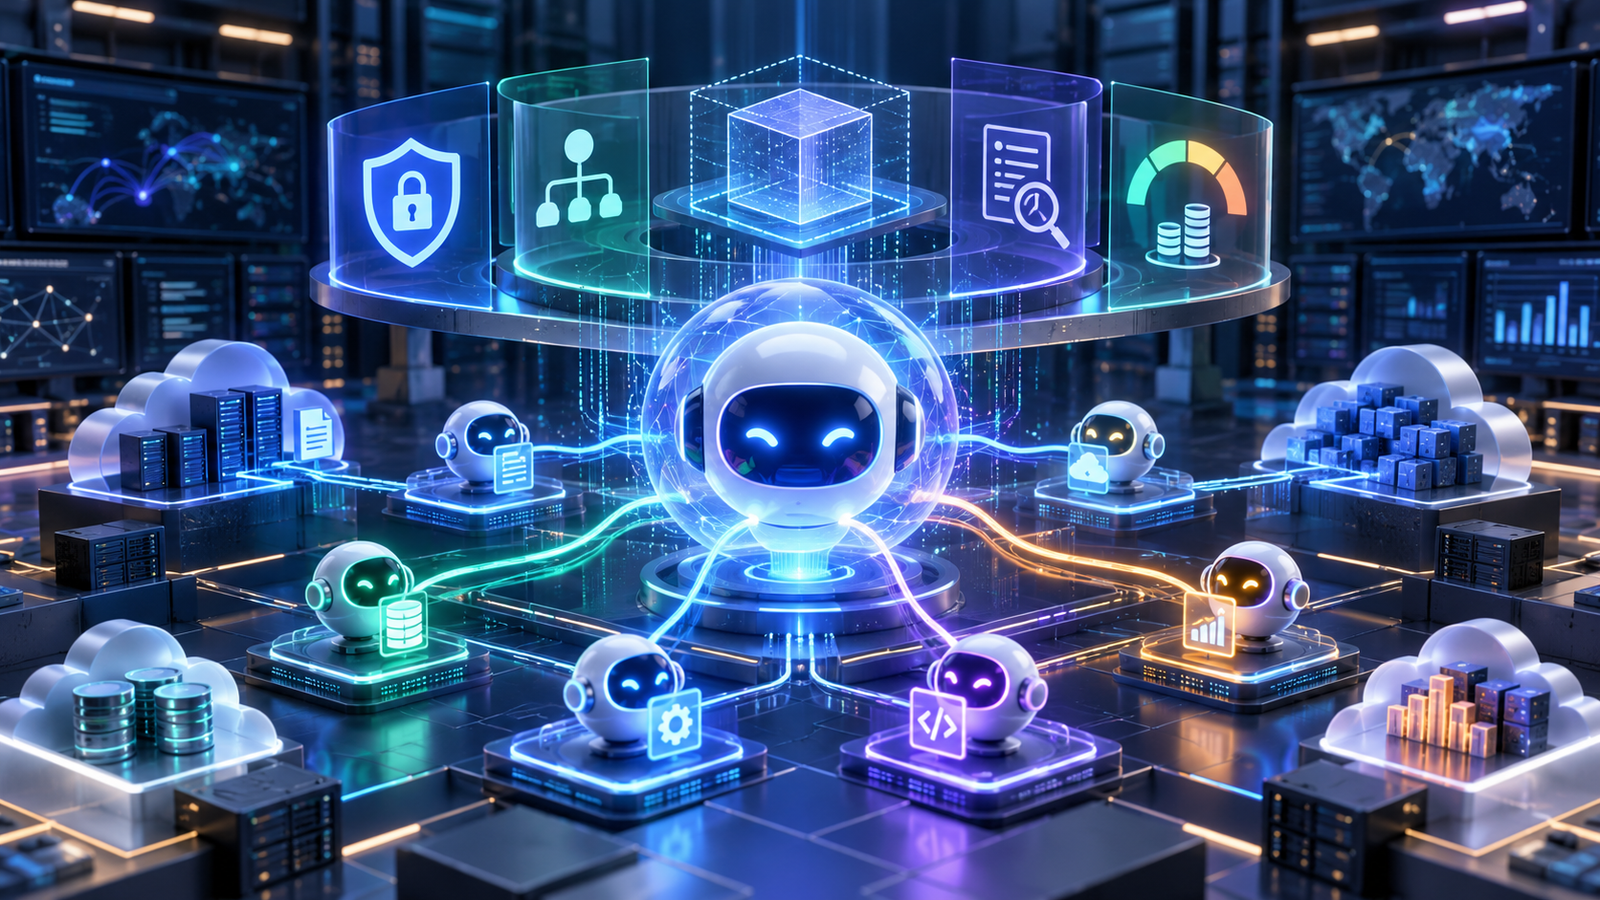
Google Cloud described Gemini agent as a single interface and API for questions, knowledge work, media creation and code execution. Users assign an objective rather than a fixed sequence of instructions, and the service can schedule work, respond to events and continue running after a laptop is closed.
The agent can also create job-specific sub-agents for parallel or sequential work. Persistent “coworker agents” receive their own identity, storage and company email address, and are limited to context shared with them. In Google Workspace, those agents can have their own account, calendar, Drive presence and directory entry rather than impersonating the employee who created them.
Google is separating the agent layer from the underlying model. The service can route work across Google’s Gemini models and Anthropic’s Claude models, with additional private and open models planned. Google says this lets difficult tasks use a stronger model while routine steps use a cheaper option. Reuters independently reported the launch and confirmed the initial multi-model support, Workspace integration and planned industry editions.
That architecture matters for teams already building LLMOps platforms. A stable agent identity, tool registry and memory layer could reduce dependence on any one model, but it also shifts testing from a single prompt-and-response path to a routing system whose behavior may change with the selected model.
Identity and policy become part of the runtime
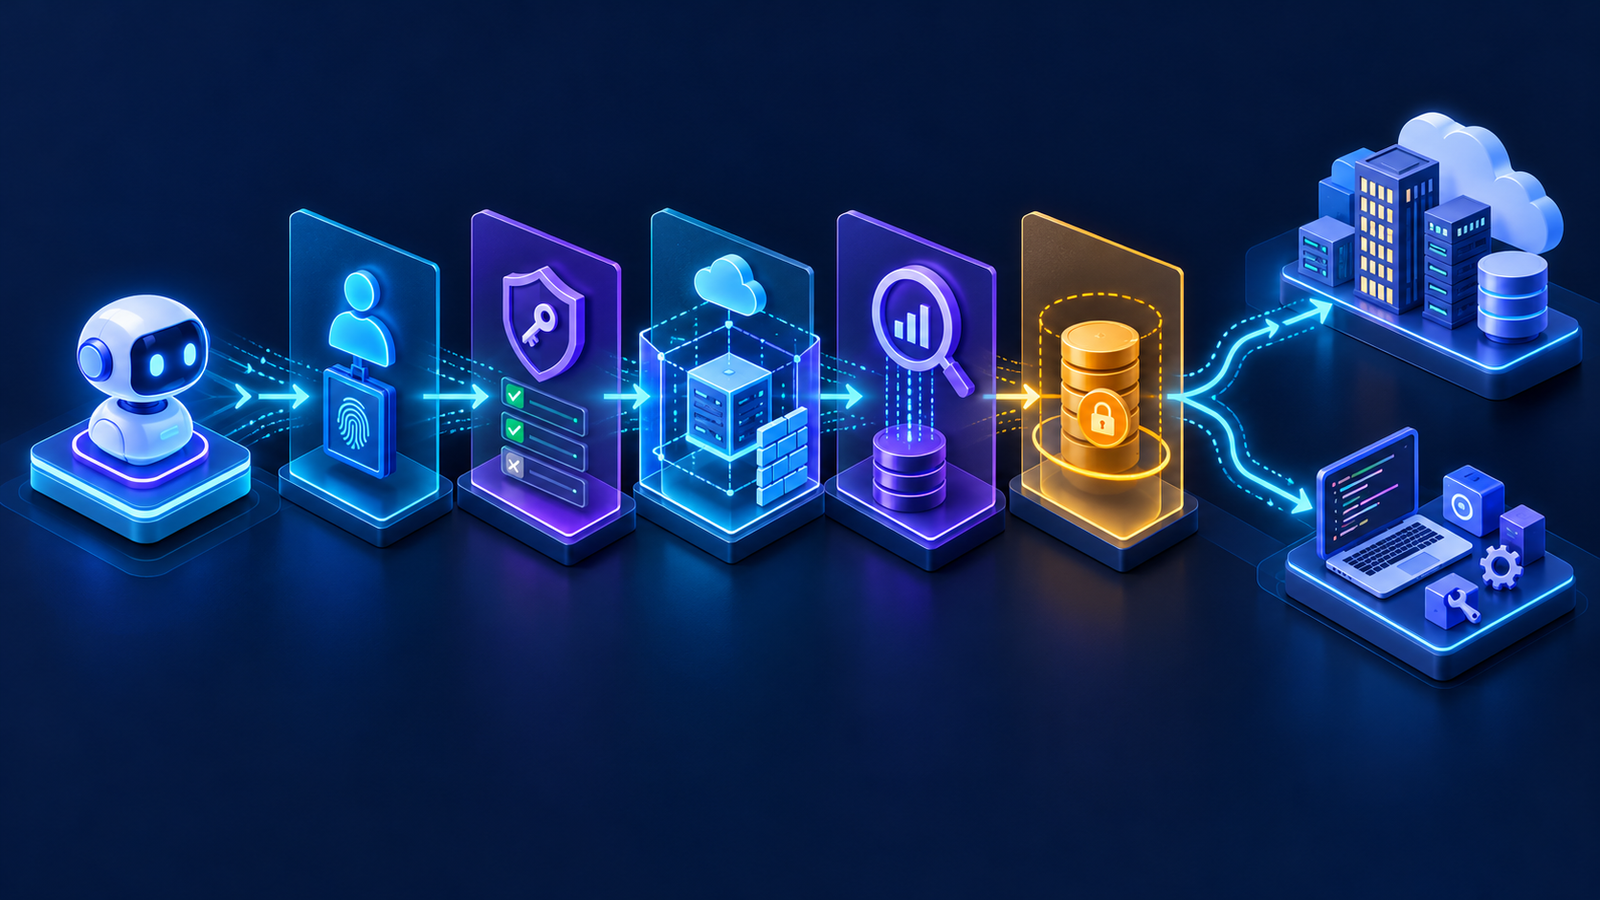
Each Gemini agent receives a cryptographically attested identity, according to Google Cloud. Administrators can grant least-privilege, role-based access, while OAuth carries that identity into external systems. Actions are written to an audit trail and attributed to the agent. The same identity is also attached to virtual machines created to execute code, which is intended to preserve traceability across the agent’s runtime.
Agent Sandbox gives each task a network boundary. Traffic entering, leaving or moving between agents passes through Agent Gateway, which Google describes as an AI network firewall that applies organization-wide policy. Google’s example is a rule preventing every agent from opening documents marked “Need to Know,” rather than configuring the restriction separately for each agent.
These controls address familiar risks, including prompt injection, excessive tool permissions, secret exposure and untracked lateral movement. They do not remove the need for independent validation. Platform teams should still treat agent-written code and tool calls as untrusted, require approval for destructive actions and test what happens when a connector, model or policy service is unavailable. GravityDevOps’ guide to AI agent security explains those boundaries in more detail.
Hard spend caps target an operational pain point
Google also introduced Smart Routing and real-time project spend caps. The routing layer selects a model based on performance and cost, while the Cloud Billing Console can enforce a hard limit covering token use and sandbox charges. When a cap is reached, the project’s agent pauses until an administrator resumes it.
That is more operationally useful than a budget alert that arrives after an autonomous workflow has already consumed resources. Google previously announced pooled quotas, pay-as-you-go agent usage and cost estimates across Gemini Enterprise and developer tools. The new launch connects those controls directly to the universal agent, although customers will need to verify how paused workflows recover, whether partially completed actions are idempotent and how chargeback data maps to teams.
What developers and DevOps teams should do next
The launch is an enterprise platform announcement, not proof that every workflow should become autonomous. Google cited deployments ranging from Orange Spain’s incident-triage agents to DBS Bank’s deterministic chains of 70 to 80 specialized agents. Those examples show the likely operating model: constrained agents assembled around governed data and narrow responsibilities, rather than one unrestricted bot controlling an entire company.
Teams evaluating Gemini agent should begin with a low-risk workflow and define the control plane before measuring productivity. That means a dedicated identity, minimal connector permissions, immutable audit logs, egress policy, human approval for consequential changes, an enforced budget and rollback procedures. Agent changes should move through the same review and CI/CD controls used for other production automation.
Availability details are mixed. The general Gemini agent was announced at Gemini at Work 2026, while specialized financial-services and legal versions are in preview; government, healthcare and retail editions are planned. Organizations should confirm regional access, licensing, connector support and feature maturity with Google Cloud before designing production dependencies around the service.
The larger signal is clear: cloud vendors are turning agent identity, execution isolation, observability and cost enforcement into first-class platform features. The competitive question is shifting from which model answers best to which control plane can safely operate persistent, multi-model workers at scale.
Sources
Primary details come from Google Cloud’s Gemini at Work 2026 announcement, its earlier description of the Gemini Enterprise Agent Platform and Google’s agent billing and cost-control documentation. The launch and competitive context were cross-checked against Reuters reporting.


