
BENGALURU, India — October 24, 2026, 6:00 PM IST — Two critical PHP vulnerabilities found with help from frontier AI systems have pushed website operators into an emergency patching cycle, while new telemetry indicates attackers were probing the flaws before their coordinated public disclosure.
The incident is becoming an operational test for a security assumption that many engineering teams still encode in policy: that a critical patch can wait for a seven-day or 30-day service-level agreement. Amazon now says the window for internet-facing systems should be measured in hours.
PHP maintainers released fixes on October 21 for CVE-2026-109618 and CVE-2026-109619, two vulnerabilities rated 9.2 under CVSS 4.0. The PHP security advisory says both flaws can permit unauthenticated remote code execution and affect PHP installations serving web requests, including PHP-FPM, Apache mod_php, php-cgi, FrankenPHP and LiteSpeed. The project says upgrading is the only complete remediation.
Exploitation began before the public advisory
Amazon Threat Intelligence reported that its MadPot honeypot network recorded a PHP2Shell exploitation attempt on October 17, four days before disclosure. Amazon observed more attempts and proof-of-concept activity on October 21 before the planned 14:00 UTC embargo expired, then saw public exploits used against its sensors almost immediately after release.
Amazon said it is unclear whether the earliest attempts would have succeeded against real production systems. The company nevertheless concluded that PHP2Shell is now being broadly exploited in the wild and advised defenders to investigate activity from at least October 17, not merely from the disclosure date.
That timeline qualifies an optimistic part of the AI-discovery story. OpenAI said frontier AI found the vulnerabilities before attackers did, to the company’s knowledge, creating what it called a defender’s window. Amazon’s later telemetry does not establish how the apparent threat actor obtained the information, but it shows that an embargo date is not a safe starting point for incident review.
What the AI systems found
OpenAI said security company Calif identified one critical flaw using GPT-5.6 Sol through its Patch the Planet initiative. Wiz independently reported both vulnerabilities and said its researchers used Wiz Atlas, Gemini 4 Argon and GPT-5.6 Sol during discovery, exploit development, detection work and patch validation.
The flaws are in PHP’s handling of fatal errors and request state. One path involves corruption after an out-of-memory condition leaves internal request data only partly initialized. The other involves internal state surviving after its backing memory has been freed and then being reused by a later request. Wiz said its researchers demonstrated pre-authentication code execution against representative WordPress, Drupal and Joomla deployments, as well as disclosure of data held in PHP worker memory.
The weakness is in the runtime rather than the application layer. That matters for platform teams because a clean application security scan does not prove that a PHP workload is safe, and changing CMS plugins or application code does not remove the vulnerable engine behavior.
Patched versions and the operational response
The PHP project lists PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 as fixed releases. PHP 8.1 and older no longer receive fixes from the upstream project, although some Linux distributions and long-term-support vendors may provide backports. The maintainers also published minimal source backports for PHP 7.4, 8.0 and 8.1 to help operators without vendor support.
On October 23, PHP issued a follow-up advisory asking operators to keep session upload progress disabled until the next regular bug-fix release unless they can rule out a narrow configuration involving serializer changes at runtime. The project described that path as unlikely in practice, but the update shows that remediation guidance can continue to evolve after an emergency release.
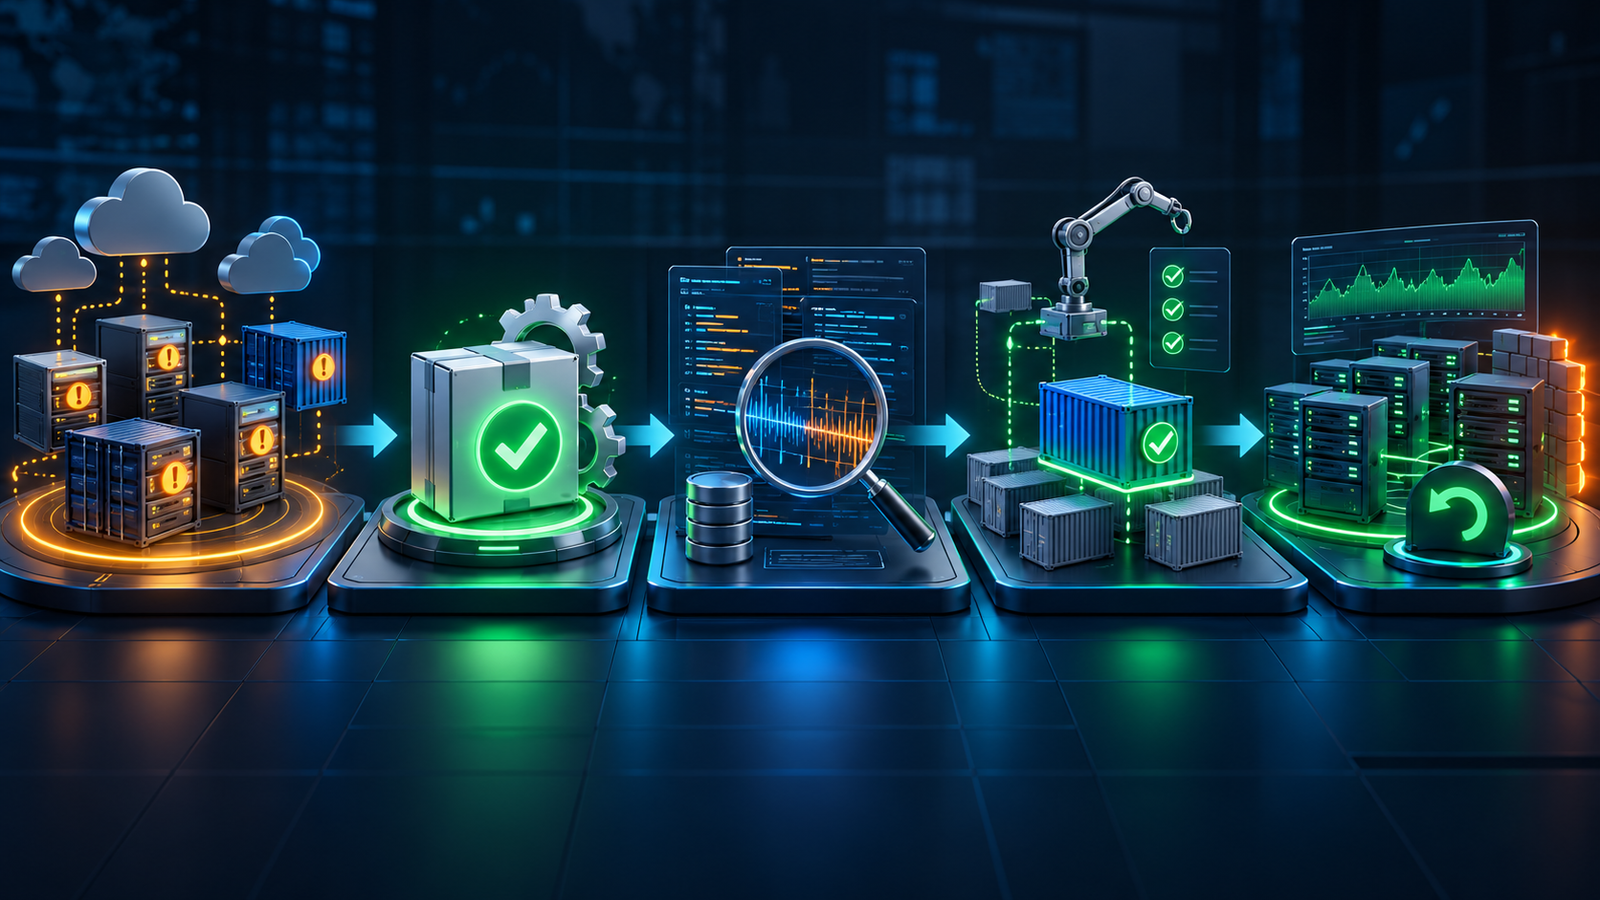
For developers, DevOps engineers and cloud platform teams, the immediate work is broader than checking a version string on one server:
- Inventory internet-facing PHP across virtual machines, containers, managed hosting, build images and dormant environments.
- Upgrade through the operating-system or runtime vendor, rebuild immutable images and confirm that newly started workers report a fixed release.
- Treat web application firewall rules and upload restrictions as temporary defense layers, not substitutes for the runtime update.
- Review request, process and file-change telemetry from October 17 onward. If investigation suggests code execution or memory disclosure, follow the organization’s incident process and evaluate credential rotation.
- Shorten emergency-patch objectives for exposed runtimes and test that asset inventory, canary deployment and rollback paths can support an hours-scale response.
AWS has published WAF mitigation guidance, but it explicitly says the edge rules support the PHP fixes rather than replace them. That distinction should also guide teams using other cloud and content-delivery providers.
A larger vulnerability-management shift
The most important longer-term development is not that AI discovered a bug. It is that the same class of systems can accelerate discovery, exploit adaptation, patch analysis and defensive validation at once.
VulnCheck’s October 22 analysis argues that AI is making advanced vulnerability research and exploitation capabilities more accessible. Reuters separately reported that researchers expect more severe findings in widely deployed software, though the timing and impact of undisclosed vulnerabilities remain uncertain.
For platform leaders, the practical conclusion is narrower and more defensible: emergency change management must assume that working exploit activity may begin before a public advisory and can scale within hours of a patch diff. Teams that already apply LLMOps controls to model deployments now need similar evidence, monitoring and rollback discipline around AI-accelerated security research. Strong CI/CD automation becomes part of the security boundary when runtime updates must move quickly without bypassing validation.
The confirmed priority remains straightforward: find exposed PHP, deploy a fixed vendor build, restart the affected workers and investigate from the earliest known activity. The broader forecast of a sustained wave of AI-found vulnerabilities is still analysis, but PHP2Shell has already shown that conventional patch clocks are too slow for the most critical internet-facing flaws.
Sources
Primary technical sources include the PHP project’s security advisories, OpenAI’s coordinated-disclosure report, Wiz Research’s technical analysis, and Amazon Threat Intelligence telemetry. Additional context came from VulnCheck and Reuters.


