
NEW DELHI, October 12, 2026, 5:00 PM IST — Anthropic has launched a free, opt-in AI vulnerability-scanning service for critical open-source projects, turning an internal security-research pipeline into a recurring service for maintainers who are prepared to review a high volume of machine-generated findings.
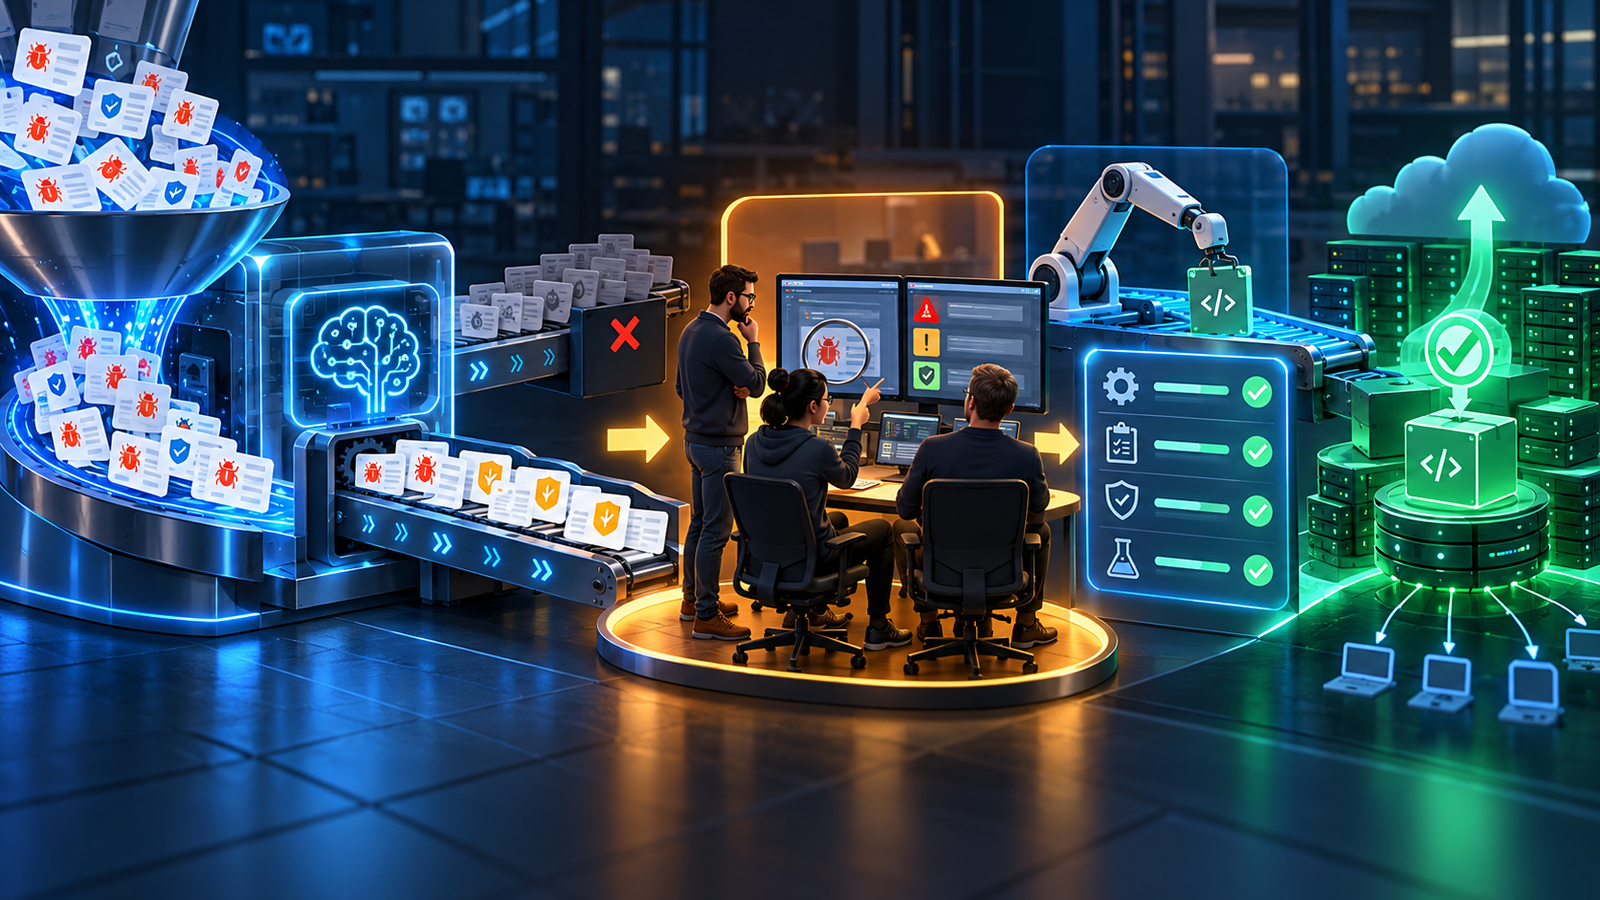
The service, called OSS Scanner, will use Anthropic’s strongest models to search enrolled codebases periodically and send maintainers reports containing a reproducer, an explanation of the weakness and, when available, a proposed patch. The reports will not receive human review before delivery. That trade-off is central to the launch: Anthropic says models can now find issues much faster than people can validate, prioritize and safely repair them.
For developers, DevSecOps teams and platform engineers, the announcement matters less as another AI coding feature than as a change in the economics of vulnerability discovery. If automated scanning produces more credible findings than maintainers can process, the operational bottleneck moves downstream to reproduction, severity assessment, patch testing, coordinated disclosure and release management.
What Anthropic confirmed
Anthropic said its models identified 29,439 candidate vulnerabilities across open-source projects during the work that preceded the service. External security firms reviewed 6,123 findings, confirming 5,674 as valid, according to the company’s coordinated vulnerability disclosure dashboard. Anthropic reported 6,157 findings to maintainers through reviewed and direct-disclosure paths, while 516 had been patched upstream as of October 2.
The figures require careful interpretation. Anthropic defines a true positive as a real vulnerability confirmed during external review, even when the issue duplicates a known report, falls outside a project’s threat model or is unlikely to be fixed. A confirmed finding is therefore not the same as a newly assigned CVE, an accepted maintainer report or a deployed patch.
In a separate validation described by Anthropic, independent penetration testers examined 97 high- and critical-severity scanner findings across 48 projects. Eighty-five met the company’s coordinated-disclosure threshold; 11 of the remaining reports concerned real issues that duplicated known problems or other scan findings, and one was invalid. Early participating maintainers cited useful findings in projects including PostgreSQL, OpenSSL, wolfSSL, curl and HotCRP.
Free access comes with a triage requirement
Core maintainers apply by submitting a pull request to Anthropic’s enrollment repository. Eligibility is decided case by case and is aimed at projects with significant infrastructure or user-security impact. Anthropic said the service is designed for projects that have enough capacity to keep up with surfaced findings; it will continue using a human-reviewed disclosure process for projects that cannot absorb raw reports.
That distinction is important. A report may include a working proof of concept and a plausible patch while still overstating severity, misunderstanding reachability or missing a project-specific security boundary. Maintainers should treat each result as untrusted security input until it is reproduced in an isolated environment and evaluated against the project’s actual threat model.
Axios reported that the unreviewed delivery model could produce inaccurate findings. Anthropic makes the same limitation explicit and says report quality, severity calibration and patch quality will need continued improvement.
A broader push into infrastructure defense
OSS Scanner is one part of a wider Anthropic Cyber Mission announced on October 8. The second component, the Critical Infrastructure Defense Program, is bringing Claude models, on-site engineers and threat research to security vendors, industrial technology providers and consulting firms that protect power, water, manufacturing and transportation systems.
The founding group includes Accenture, Booz Allen, CrowdStrike, Deloitte, Dragos, Hitachi, Nozomi Networks, Palo Alto Networks, PwC and Rockwell Automation, among others. Anthropic said several partners are already using Claude to identify and repair vulnerabilities. It did not publish program-wide pricing, deployment architecture or measurable remediation targets.
Operational technology adds a constraint that ordinary application teams do not always face: a safe patch may require planned downtime, vendor certification or physical-site coordination. Axios noted that the announcement leaves open how participants will test and deploy fixes without disrupting essential services. Anthropic also acknowledged that AI cannot solve many of the structural problems involved in defending aging industrial systems.
What DevOps and platform teams should change
The immediate lesson is not to replace existing scanners or security review with an AI queue. Teams consuming open-source components should prepare for more upstream findings and faster patch proposals while keeping deterministic controls around acceptance and rollout.
A practical operating model is to route machine-generated reports into a separate intake lane, deduplicate them against existing advisories, reproduce them in disposable environments, confirm affected versions and reachability, then require normal code review and CI checks before merge. High-impact fixes should pass regression, fuzzing and canary stages before broad deployment. These controls fit naturally into a mature CI/CD pipeline and a broader LLMOps operating model.
Software composition analysis remains necessary because discovery and exposure are different questions. A scanner may find a flaw in an upstream repository, but teams still need an accurate software bill of materials, dependency reachability, deployed-version inventory and ownership records to determine where remediation is urgent.
What remains uncertain
Anthropic has not disclosed how many projects the scanner can support, how frequently each repository will be scanned or what service levels maintainers should expect. The company also has not provided an independent, ecosystem-wide measure of false positives, patch acceptance or time to remediation. Its public results are promising evidence from its own program, not proof that unreviewed AI findings will scale cleanly across every language and project.
The launch nevertheless establishes a concrete test for AI-assisted security: whether models can reduce exploitable open-source risk without shifting an unmanageable verification burden onto volunteer maintainers. For engineering organizations, the near-term advantage will go to teams that can turn a faster stream of findings into verified, tested and observable fixes.
Sources
Anthropic’s Cyber Mission announcement, its OSS Scanner technical launch post, the company’s coordinated vulnerability disclosure dashboard, and Axios reporting on the program.

