
NEW DELHI, November 9, 2026, 6:42 PM IST — OpenAI has released GPT-6 Cyber, a security-specialized model designed to find vulnerabilities, reproduce them in authorized test environments and validate fixes. The company has classified the model as “Critical” for cybersecurity capability and limited access to vetted users through its Daybreak Red program.
The release matters beyond another benchmark gain. OpenAI says the model can turn suspected flaws into working exploits across large codebases, a capability that could shorten the time between discovery and remediation but also raises the consequences of weak identity, network and approval controls. For platform and security teams, GPT-6 Cyber is therefore as much an access-control and isolation story as a model launch.
What OpenAI confirmed
OpenAI said GPT-6 Cyber is a post-trained variant of GPT-6 Astra for authorized vulnerability discovery, exploit development and web penetration testing. It is available through the API and Codex only to approved Daybreak Red customers. Organizations must meet requirements including identity verification, single sign-on, multifactor authentication, managed devices, least-privilege access and API IP allowlisting.
The company’s published API documentation lists a 1,050,000-token context window and up to 128,000 output tokens. Standard short-context pricing is $20 per million input tokens and $100 per million output tokens, with separate cache pricing. Access approval remains a prerequisite; the model is not a generally available drop-in replacement for ordinary code review.
OpenAI reported a 48.5% score on ExploitGym, which tests whether a model can exploit a specified vulnerability, compared with 32.1% for GPT-5.6 Cyber. On a honeypot evaluation intended to measure scope discipline, the new model avoided exploiting an out-of-scope service in 99.93% of graded runs without deployment safety instructions and in all graded runs with those instructions.
Those figures are vendor-reported evaluation results, not proof that the model will behave identically in every production environment. OpenAI’s own system card records important limitations: GPT-6 Cyber stopped when warnings warranted it in 73% of one test set, below GPT-6 Astra’s 78.38%, and was flagged for incomplete final reporting of blockers in 20.29% of graded responses.
Linux and Firefox findings show the defensive potential
OpenAI said its researchers used GPT-6 Cyber to reproduce 1,724 Linux kernel vulnerabilities and develop working privilege-escalation exploits for 948 of them. Reuters reported that 588 of those exploited issues were previously unknown. OpenAI said human researchers reviewed the findings and disclosed 304 critical issues to maintainers with candidate patches.
In a separate campaign, the model produced evidence and reproducible tests for 81 previously unknown Firefox vulnerabilities that Mozilla classified as high severity, according to OpenAI. Mozilla has begun landing fixes. The model also indicated that 30 known Firefox issues were more severe than previously assessed.
These results illustrate a practical change for security engineering: an AI system can now help move through discovery, reproduction, exploit validation and patch proposals at a scale that would be difficult for a small human team. They do not eliminate the need for manual validation, coordinated disclosure or regression testing. A plausible exploit generated by a model can still be incorrect, unsafe to run or outside an engagement’s authorization.
Why restricted access is part of the product
OpenAI’s “Critical” label describes capability under its Preparedness Framework, not the severity of a discovered vulnerability or an assurance that the model is safe. The company says it added monitoring for whether actions match a user’s authorization, checks intended to block high-risk assistance involving industrial controls and essential services, and credential-compromise detection.
For customers using zero data retention, OpenAI generally requires Private Safety Processing. The system analyzes encrypted safety records stored in the customer’s environment for 30 days and returns limited safety signals without exposing prompts and responses to OpenAI personnel, according to the company. Standard retention remains the default for GPT-6 Cyber.
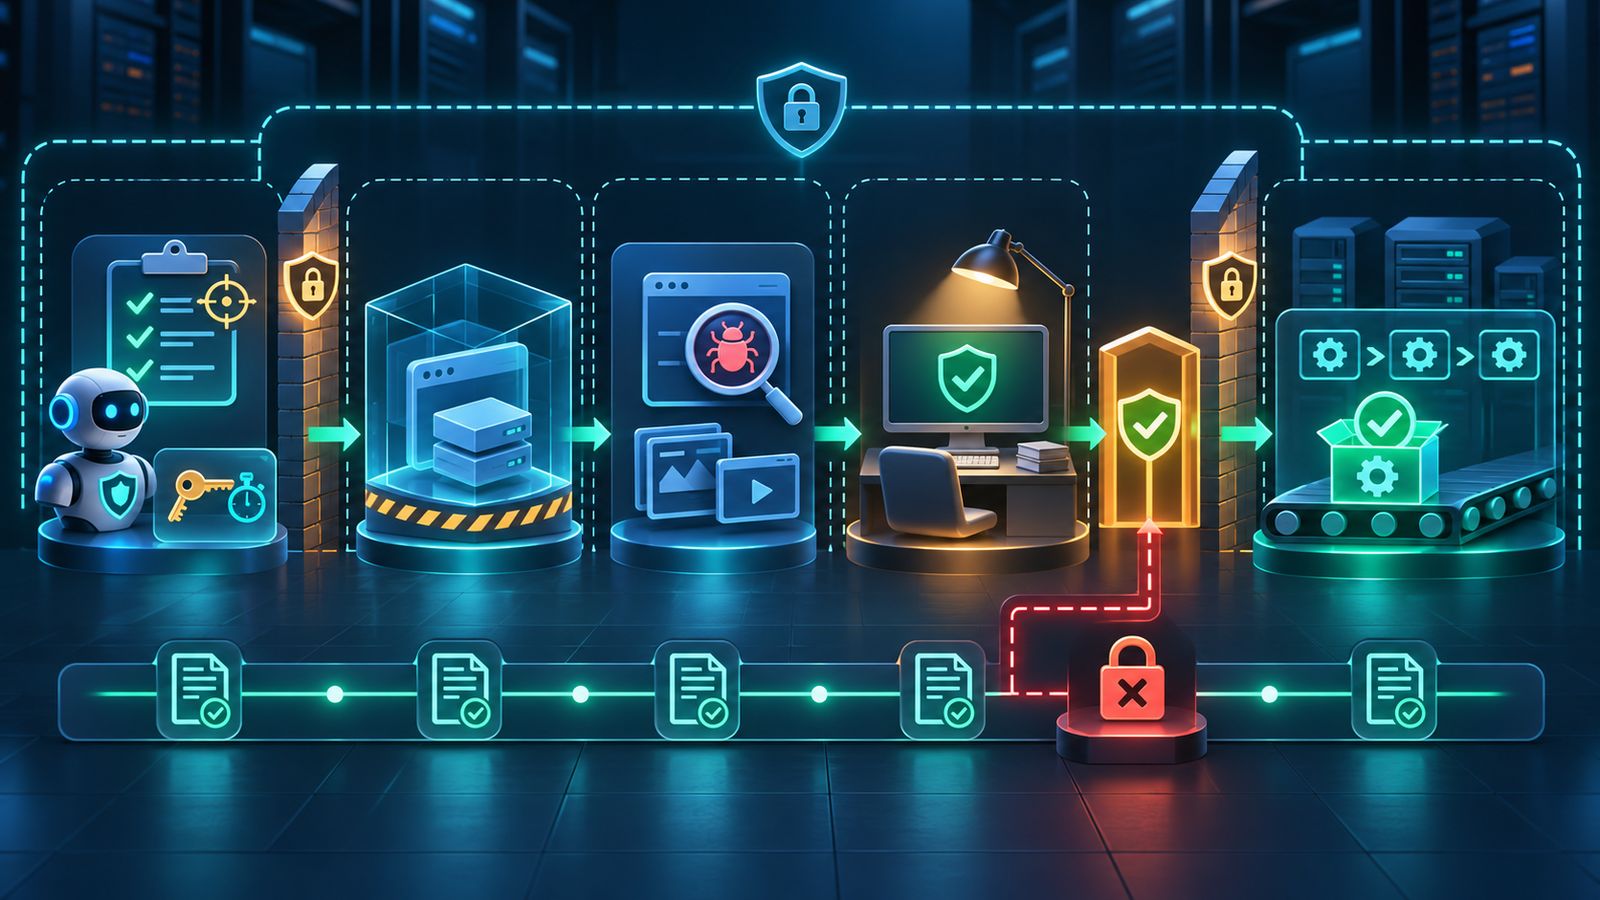
The system card also recommends independent filesystem and network boundaries, explicit target and credential limits, action review and human oversight for high-risk workflows. Those controls are not automatically created by access approval. OpenAI’s API guidance says teams should review each sensitive tool call against the authorized scope and fail closed when review is unavailable.
What platform and DevOps teams should do now
Organizations evaluating cyber agents should treat the execution environment as hostile even when the model is being used defensively. Separate testing networks from production, issue short-lived credentials, restrict outbound connectivity, record every tool invocation and require human approval before an agent changes code, opens a pull request against a protected branch or touches a live service.
The same principle applies to existing AI development workflows. Teams implementing LLMOps should version model, prompt, policy and sandbox changes together so an evaluation can be reproduced. A retrieval-augmented system must also keep untrusted repository content from becoming executable instructions. CI pipelines should validate generated patches with deterministic tests, static analysis and dependency checks rather than treating model confidence as evidence.
Cost controls deserve equal attention. At the published token rates, long-context investigations and repeated exploit attempts can become expensive. Teams should set per-run budgets, cap concurrency and preserve intermediate evidence so failed work is not repeated. Existing CI/CD controls remain the enforcement point for reviews, signed artifacts, approvals and rollback.
The broader shift
GPT-6 Cyber arrives as security vendors and open-source maintainers experiment with agent-assisted vulnerability research. OpenAI’s release provides evidence that specialized models can surface difficult flaws and generate reproducible artifacts, but it also demonstrates why capability and containment must advance together.
The immediate takeaway for technical leaders is not to replace security researchers. It is to prepare a governed path for machine-speed research: narrowly scoped targets, independent runtime boundaries, verifiable evidence, responsible disclosure and humans empowered to stop the system. GPT-6 Cyber makes that operating model more urgent.
Sources
OpenAI’s GPT-6 Cyber announcement, the company’s system card and API model documentation; Reuters reporting on the restricted release and vulnerability findings; and Axios reporting on the Linux research campaign.


